Understand your suppliers’ cyber risk. Strengthen your resilience.
RiskRecon by Mastercard gives your organisation continuous visibility into suppliers’ externally observable cybersecurity posture—helping you prioritise risks, guide remediation and support your NIS2 and ISO 27001 risk-management activities.
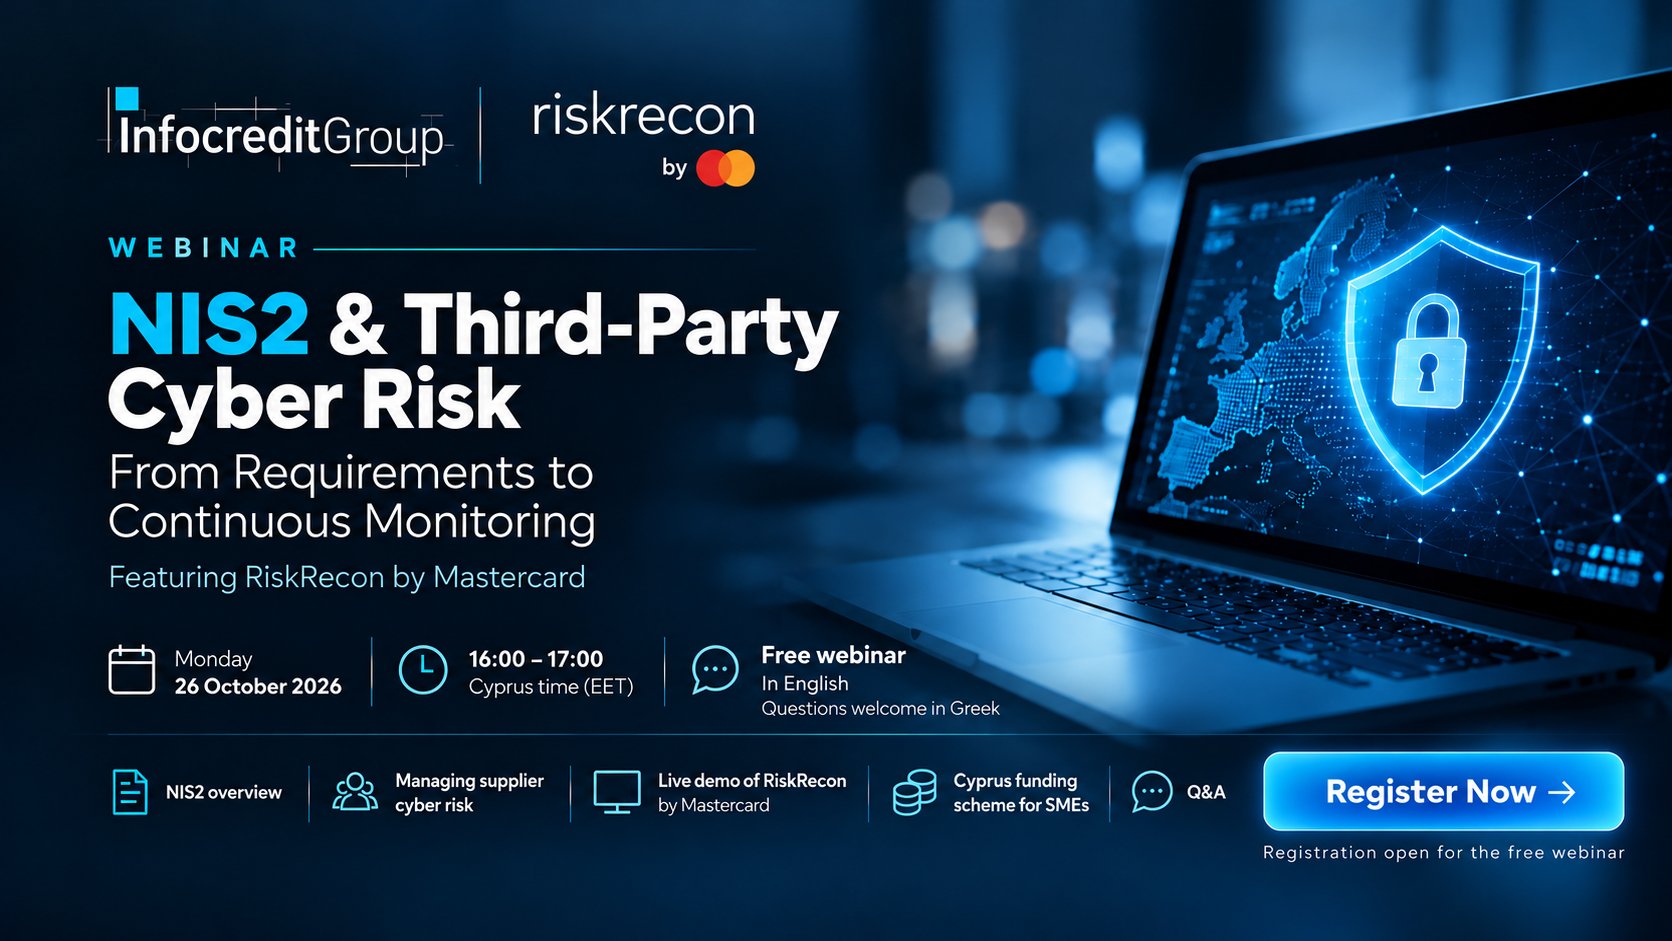
Free online webinar
NIS2 & Third-Party Cyber Risk: From Requirements to Continuous Monitoring
Featuring RiskRecon by Mastercard
Monday, 26 October 2026 · 16:00 – 17:00 Cyprus time (EET) English (questions welcome in Greek)
What RiskRecon gives your team
RiskRecon assesses suppliers’ internet-facing systems — what can be observed from outside — and turns the results into an objective rating and prioritised findings. It is an external view: it complements, rather than replaces, a full review of a supplier’s internal security controls.
Assess suppliers before onboarding
Review a prospective supplier's internet-facing security posture before you sign the contract.
Continuously monitor cybersecurity ratings
Ratings refresh as suppliers' internet-facing systems change, between your formal review cycles.
Identify changes in security posture
See when a supplier's externally observable posture improves or deteriorates.
Prioritise findings and remediation
Findings are weighted by the value of the affected asset, giving you a focused basis for supplier remediation discussions.
Compare vendors consistently
Rate suppliers on one consistent framework so you can compare them across your portfolio.
Support reporting and supplier reviews
Use ratings and documented findings in management reporting and periodic supplier reviews.
Support your NIS2 and ISO 27001 readiness
Supplier cybersecurity needs ongoing attention. RiskRecon provides external security insights that can inform your organisation’s wider governance, due diligence and risk-management processes.
NIS2 readiness
Strengthen your approach to supply-chain cyber risk with consistent supplier assessments, ongoing monitoring and prioritised findings to inform risk treatment.
ISO 27001 supplier security
Support supplier risk assessments and ongoing reviews with documented cybersecurity findings and monitoring insights that complement your information security management system.
RiskRecon supports selected risk-management activities. It does not independently establish NIS2 compliance or provide ISO 27001 certification.
Start with the suppliers that matter most
- 01
Identify your critical suppliers and service providers.
- 02
Assess their externally observable cybersecurity posture.
- 03
Prioritise findings and engage suppliers on remediation.
- 04
Monitor changes and review risk over time.
See RiskRecon in action
Discuss your supplier portfolio with Infocredit Group and discover how continuous cybersecurity monitoring can support your risk-management programme.
Frequently asked questions
What does RiskRecon assess?
RiskRecon assesses a company's internet-facing systems — such as websites, domains, email and network services — across multiple security domains. It is an external view and does not audit a supplier's internal security controls.
How does continuous monitoring support supplier reviews?
Ratings update as a supplier's externally observable posture changes, so you can spot deterioration between reviews and bring current, documented findings into each supplier discussion.
How can RiskRecon support NIS2 readiness?
It can inform your supply-chain risk management with consistent supplier assessments, ongoing monitoring and prioritised findings that feed into your risk treatment decisions.
How can it support ISO 27001 supplier risk management?
Its documented findings and monitoring insights can support supplier risk assessments and ongoing supplier reviews within your information security management system.
Does RiskRecon guarantee compliance or certification?
No. RiskRecon supports selected risk-management activities. It does not independently establish NIS2 compliance or provide ISO 27001 certification.
How does Infocredit Group help with implementation?
Infocredit Group handles onboarding, setting up your supplier portfolio, training your team and ongoing local support for the RiskRecon platform.